For Brazilian firms running AI in regulated environments, data sovereignty determines where sensitive information is processed, who can access it, and which rules govern the service. Keeping workloads in Brazil can simplify oversight and reduce cross-border exposure, but location alone does not establish compliance. A sound approach maps the whole AI workload, from prompts and model files to logs, backups, and support access.
Key points for decision-makers
- AI sovereignty applies to data, models, compute, operational access, and service governance.
- Brazilian law permits international data transfers under specified conditions, so residency and transfer compliance are related but distinct questions.
- Financial institutions should assess cloud and technology providers through their own governance and risk processes.
- Workload mapping helps teams identify where sensitive data or artifacts could cross borders.
- Brazil-based GPU infrastructure can support local control, while contractual terms and operational practices still require review.
AI sovereignty covers the whole production workload
AI data sovereignty means an organization can understand and govern the location, access, and handling of data and related assets used by its AI systems. The scope extends beyond the original customer record to include prompts, embeddings, model checkpoints, audit logs, backups, and telemetry.
This matters because production AI infrastructure combines compute, storage, networking, orchestration, and monitoring. A workload may run inference in one location while its logs, vector database, backups, or support tools operate elsewhere. A provider's regional label alone does not show how every component is handled.
For a bank reviewing transactions, for example, the relevant map includes input records, inference requests, model versions, decision logs, and the systems that retain them. A fintech deploying a customer-service agent must also consider retrieved documents, conversation histories, and the agent's access to internal tools.
Brazilian law allows transfers under defined conditions
Data residency and legal compliance are connected, but they are not interchangeable. Brazil's LGPD sets conditions for international transfers rather than establishing a blanket rule that all personal data must remain in the country. The law's transfer provisions are available in the official text of the LGPD.
The ANPD's international transfer regulation and standard contractual clauses give organizations additional mechanisms to assess and document qualifying transfers. A firm should therefore identify whether a provider, subprocessor, support team, or backup service can access personal data from abroad, then confirm the applicable legal basis and safeguards with its privacy and legal teams. The ANPD announcement on international transfers summarizes the regulator's framework.
Keeping compute and data in Brazil can reduce the number of cross-border flows that need to be assessed. It does not remove the need for a lawful purpose, access controls, retention limits, security measures, and clear accountability.
Data location is only one part of sovereignty
Organizations gain a clearer view of sovereignty when they examine the full service boundary. The key questions concern where assets reside, who can reach them, how controls are evidenced, and what happens if the service changes.
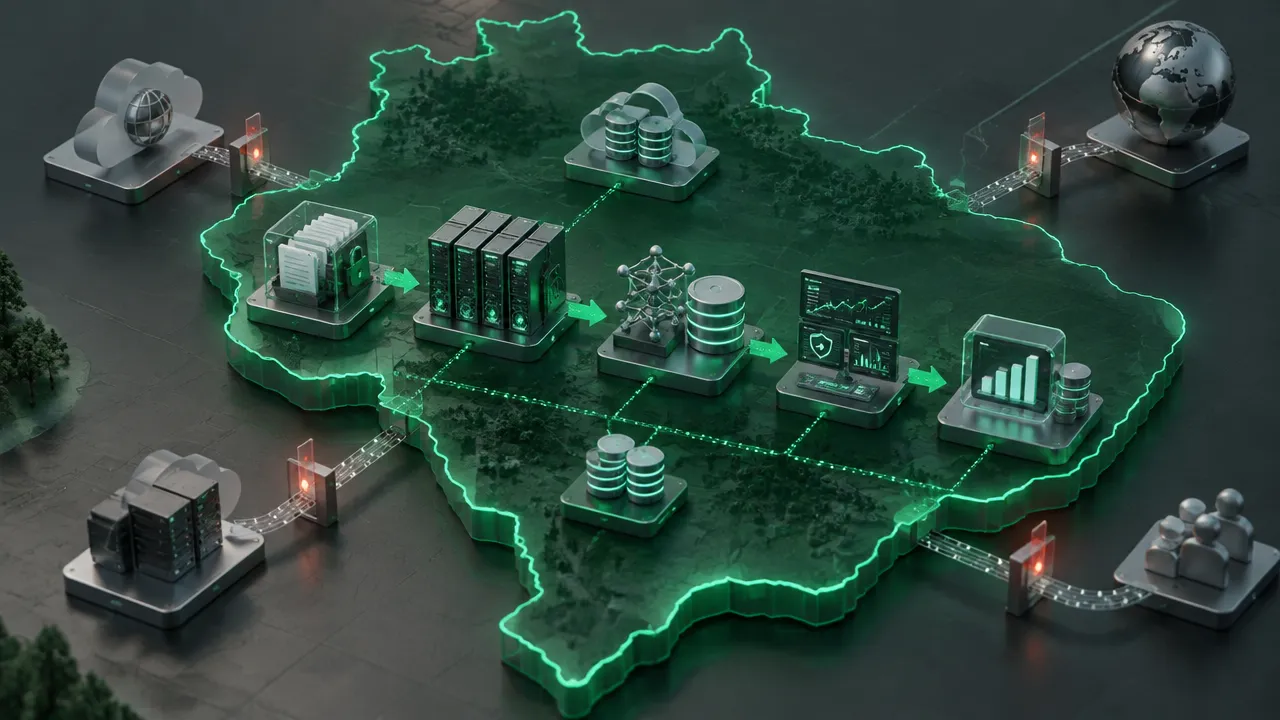
A practical inventory should cover:
- Data: source records, prompts, retrieved documents, embeddings, outputs, and retention periods.
- AI assets: model weights, fine-tuning datasets, checkpoints, and evaluation results.
- Operations: logs, metrics, backups, incident records, and administrator access.
- Service chain: subprocessors, support locations, orchestration services, and external integrations.
- Exit: export formats, deletion evidence, transition support, and the handling of retained copies.
This map gives security, privacy, legal, and infrastructure teams a shared view of the workload. It also reveals dependencies that may be missed when procurement evaluates only the GPU region.
Local processing can reduce specific operational risks
Brazil-based processing can reduce exposure to cross-border data movement and may help teams align service operations with Brazilian oversight. It can also shorten the network path for users and systems located in Brazil. These are potential design benefits, not automatic guarantees of compliance, resilience, or lower cost.
Operational risk can still arise from weak identity controls, excessive retention, unencrypted backups, insufficient incident procedures, or unclear provider access. Sovereignty therefore depends on both location and enforceable controls. Contracts should explain responsibility for access approval, incident notification, audit evidence, deletion, and service continuity.
Financial institutions should include cloud and technology services in established supplier-risk processes. The Central Bank of Brazil's CMN Resolution 4,893 provides a regulatory reference for cybersecurity and relevant technology-service arrangements. Firms should confirm the current requirements and applicability with their compliance teams.
Workload mapping turns sovereignty into a design decision
Before selecting a platform, teams can classify each workload by data sensitivity, processing purpose, latency needs, and operational impact. That classification helps distinguish cases that require strict local processing from workloads that can use other arrangements after legal and security review.
- Trace the data path. Follow each input through inference, retrieval, logging, storage, backup, and deletion.
- Identify access paths. Document human administrators, support personnel, service accounts, and subprocessors.
- Set evidence requirements. Specify what records, audit logs, contractual commitments, and incident reports the provider must supply.
- Test failure and exit plans. Confirm how workloads can be restored, moved, or shut down, and how data copies are removed.
- Review the economics. Estimate GPU use, storage, networking, support, and currency exposure over realistic demand cycles.
This process links sovereignty to the wider AI infrastructure design: data governance, model deployment, GPU orchestration, observability, and cost management must fit together. A system that meets a residency goal but cannot be monitored or recovered is not ready for production.
Provider evaluation should test controls, not slogans
A useful provider review asks for evidence about the actual service configuration. Teams should check the locations of compute and storage, the treatment of logs and backups, support access, subcontracting, incident handling, and the ability to export and delete assets. Those details are more actionable than a general statement that a platform is secure or sovereign.
For financial workloads, governance also includes change management, access review, continuity planning, and clear responsibility between the institution and provider. These checks should fit the organization's existing risk framework rather than sit in a separate AI-only process.
Cost belongs in the review because infrastructure decisions can affect both budgets and operational choices. GPU billing, storage, data transfer, and foreign-exchange exposure can change the total cost of operating a workload. A local service billed in Brazilian reais may simplify budgeting for some firms, but the full service scope and usage assumptions still need comparison.
Brazil-based GPU infrastructure can support local control
Nuplia provides managed GPU-as-a-Service and AI inference infrastructure in Brazil for organizations operating regulated workloads. Its offering includes elastic, hourly billed NVIDIA GPU capacity, including RTX PRO 6000 Blackwell GPUs for inference and fine-tuning, with Kubernetes and GPU orchestration.
For teams assessing sovereignty, relevant service details include where compute and data reside, how operational access is governed, and what contractual evidence is available. Nuplia also provides support in Portuguese, invoices in Brazilian reais with NF-e, and charges no egress fees, according to the service brief. Those features can support local operations and cost planning, while each customer remains responsible for confirming that a specific architecture meets its legal and internal requirements.
The most reliable path is to start with the workload map, define the controls each data category requires, and then assess infrastructure against those requirements. For Brazilian firms, sovereignty becomes practical when legal obligations, system architecture, provider operations, and exit planning are reviewed together.